A public HTTPS URL for any local port — over plain SSH.
One command. A live address on tunnelize.it that forwards to your machine for as long as the SSH session stays open.
What you get
Exactly this — nothing more to set up.
Public HTTPS URL
Something like https://happy-tiger-a1b2c3d4.tunnelize.it, valid while your SSH session is open.
Terminal request log
Path, status, size, timing, visitor IP — printed live in the same session.
Fixed URL (optional)
Connect as static@. Same subdomain every time, from your SSH key. No account.
Visitor password (optional)
Connect as auth@. HTTP basic auth; password shown in your banner.
How it works
SSH reverse-forwards a port. tunnelize.it puts HTTPS in front.
Your client opens an outbound SSH connection. The edge terminates TLS, then sends each request down that tunnel to localhost on your machine.
Visitor
Opens https://happy-tiger-a1b2c3d4.tunnelize.it
tunnelize.it edge
Certificate, phishing warning, rate limits — then proxy into the tunnel
Your machine
SSH session you started · localhost:3000
No inbound ports, no agent install, no account. Close the terminal and the URL dies with it.
One-liner
Don’t want to type the ssh command?
Paste one of these. It downloads a short script, asks for your local URL, and starts the same tunnel as above.
Windows gets PowerShell; Mac and Linux get bash. Open
https://tunnelize.it/proxy
in a browser to see both commands as plain text.
Windows — PowerShell
Run in the current session.
irm https://tunnelize.it/proxy | iex
Linux / macOS — curl + bash
Pass your local URL after --.
curl -fsSL https://tunnelize.it/proxy \
  | bash -s -- http://127.0.0.1:8080
Need a fixed URL or a visitor password? Add it to either one-liner above:
https://tunnelize.it/proxy?mode=static — same address every time
https://tunnelize.it/proxy?mode=auth — visitors must enter a password
In the GUI below, choose that under Mode.
Windows — PowerShell GUI
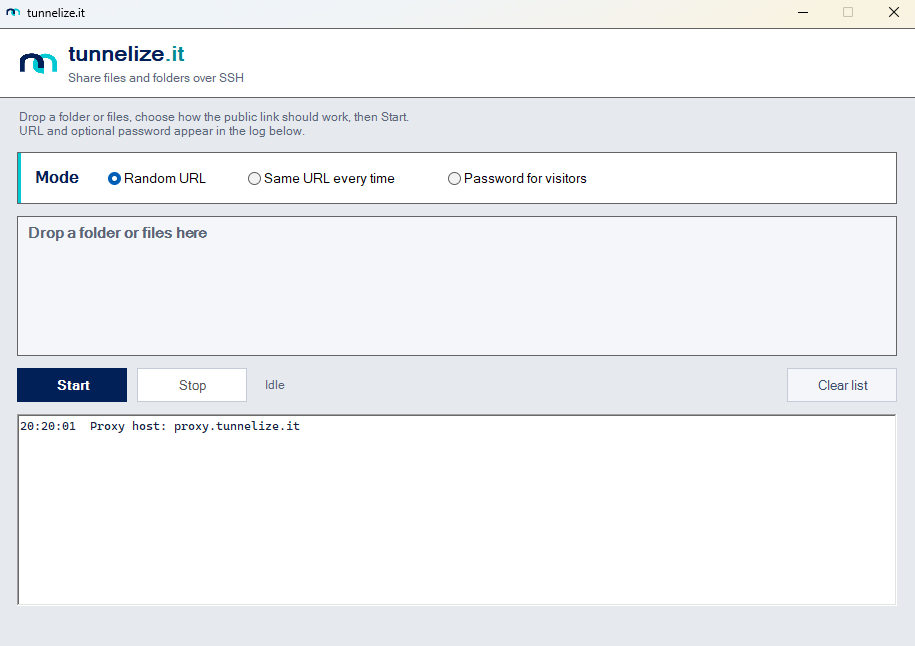
Share files or a folder: drop them in, choose random / fixed / password, hit Start. Built-in mini server — no extra modules.
irm https://tunnelize.it/proxygui | iex
Modes
Three ways to connect. Same tunnel underneath.
Pick the SSH user. Everything else — HTTPS, request log, WebSockets — stays the same.
Random URL
ssh -t -R 80:localhost:3000 proxy.tunnelize.it
New subdomain each session. Fine for a quick share.
Fixed URL
ssh -t -R 80:localhost:3000 [email protected]
Same address every reconnect, derived from your SSH public key. Any key works; nothing to register. Without a key, static@ is refused.
Visitor password
ssh -t -R 80:localhost:3000 [email protected]
HTTP basic auth for browsers. Username is always tunnelize; a short password is printed in your terminal for that session.
Where it fits
Anything that needs to call your laptop.
Webhooks
Stripe, GitHub, Slack — point the callback at a fixed tunnelize.it URL and debug on your machine.
Live demos
Send a teammate or client the HTTPS link. Hot reload still works over the tunnel. Add a password if the link shouldn’t be open.
Phones & devices
Open your dev server on a real phone over mobile data — same public URL, no LAN gymnastics.
OAuth & CI
Redirect URIs and CI callbacks need a stable HTTPS host. Use static@ and configure it once.
Files & folders
Need a quick download link? The Windows PowerShell GUI (/proxygui) serves a dropped folder over HTTPS while the session is open.
Compare
When plain SSH is enough.
tunnelize.it is for “I need a URL now” — no agent, no signup, free fixed URLs and visitor passwords included.
| tunnelize.it | ngrok | Cloudflare quick tunnel | |
|---|---|---|---|
| Client | SSH only | Agent | cloudflared |
| Account | None | Required | Optional |
| Same URL every time | Free via SSH key | With account | Account + own domain |
| Visitor password | Built in | Paid / config | No |
| Price | Free | Free tier + paid | Free |
FAQ
Straight answers.
What people ask before the first tunnel.
What do I actually get?
https://<subdomain>.tunnelize.it address for one local port, for the lifetime of your SSH session. Plus a live request log in that terminal. Close SSH and the URL is gone (unless you reconnect with static@ for the same fixed name).Is tunnelize.it free?
Do I need to install anything or create an account?
Is there a helper script?
irm https://tunnelize.it/proxy | iex
curl -fsSL https://tunnelize.it/proxy | bash -s -- http://127.0.0.1:8080
irm https://tunnelize.it/proxygui | iex
First: Windows PowerShell (local HTTP app). Second: Linux / macOS. Third: Windows PowerShell GUI to share files or a folder. For
/proxy, append ?mode=static or ?mode=auth; force the OS with ?os=windows or ?os=linux.
The GUI picks the mode in the window.
On Windows, if direct SSH is blocked, the PowerShell launchers fall back to a WebSocket bridge at wssproxy.tunnelize.it (still OpenSSH underneath; set TUNNELIZE_TRANSPORT=wss to force it).
Can I share files or a folder without a web server?
irm https://tunnelize.it/proxygui | iexDrop files or a folder into the window, pick random URL / fixed URL / visitor password, then Start. The script serves them locally and opens the same SSH tunnel; visitors get a normal HTTPS download link. No IIS, no Node, no extra modules — just PowerShell. Close the window and the link is gone.
Can I keep the same URL every time?
[email protected] (or /proxy?mode=static). The subdomain is derived from your SSH public key. Only that private key can claim it.Can I password-protect the tunnel?
[email protected] (or /proxy?mode=auth). Visitors get HTTP basic auth; username is tunnelize; the password is printed in your terminal banner.Can I choose the subdomain?
static@ you get a new random name each session.Do WebSockets work?
Why do visitors see a warning page?
curl, and other non-browser clients skip it. Browser-like clients can send the tunnelize-skip-browser-warning header.Is traffic encrypted?
HTTP or HTTPS to my local app?
-R 80 and -R 443 are accepted (left-hand bind port). 80 probes your target once and uses HTTP or TLS accordingly. 443 always speaks TLS to the app (self-signed is fine). The local port on the right can be anything, e.g. -R 80:localhost:3000 or -R 443:localhost:8443.My dev server says “Blocked request” / “Invalid Host header”
.tunnelize.it in that server’s host config.